
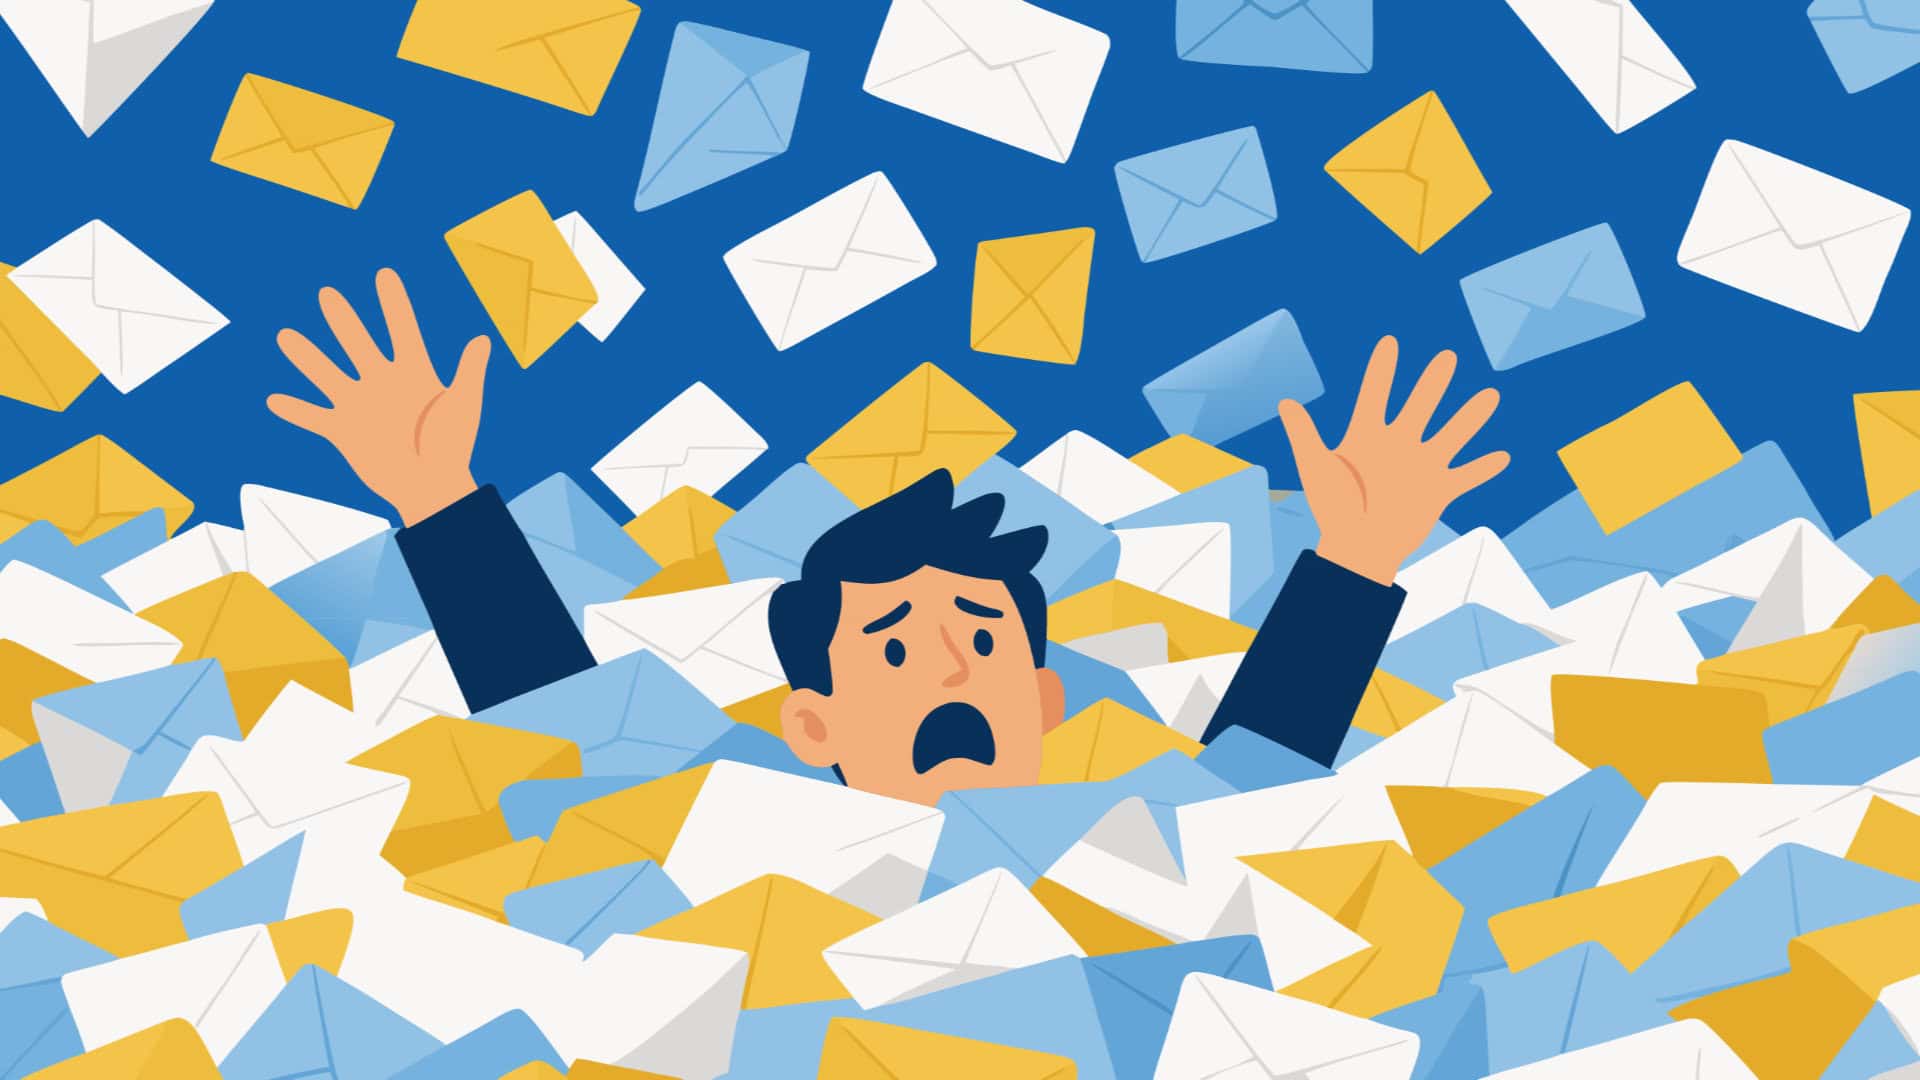
Our email security experts are currently noting an increase in a particularly devious multi-vector attack. First, cybercriminals flood employees’ personal email inboxes with emails that appear (technically) harmless. This is soon followed by contact from a person claiming to belong to IT support – often via Microsoft Teams – who then attempts to trick the user into revealing their login credentials / MFA codes or installing a remote access tool.
Here’s how the attack proceeds
Attackers bombard email accounts with newsletter subscriptions, automated notifications, or other messages that are essentially harmless. These emails are primarily sent via transactional email services using various sender-recipient combinations. They also utilize a number of different subdomains and “plus addresses”. This creates a multitude of distinct sending patterns, making it difficult for conventional security filters to identify the messages as belonging to a wave of attacks.
From a purely technical standpoint, the individual emails are generally no cause for alarm. They are properly authenticated, don’t contain any harmful links or attachments, and tend not to display the typical characteristics of a phishing email. For the algorithms that typically evaluate messages individually, the actual intent behind them is thus largely well concealed.
Aiming to take advantage of the bewilderment caused by the flooded inbox, the attackers then contact the victim (for instance, via an external Microsoft Teams call or chat), posing as internal IT support and offering their “help”.
Why classic spam protection is not enough on its own
“Inbox bombing” deviously combines several channels in a single attack. Effective protection therefore requires a combination of maximum email traffic transparency, rapid forensic analysis, and the ability to respond instantly.
That’s why Retarus Email Security tackles the attack chain at multiple points. Firstly, the company’s various anti-spam and anti-phishing filters significantly reduce the likelihood that suspicious or malicious content will end up in a user’s inbox. In addition, Directory Harvest Attach (DHA) Protection impedes the attackers’ ability to harvest personal email addresses. Finally, Backscatter Protection prevents the attack from being amplified by automated response messages.
Maximum data transparency makes anomalies visible
As long as the individual messages are properly authenticated and contain no malicious links or attachments, this type of inbox-bombing campaign can’t be detected reliably based on content and formatting alone. This is where the high level of transparency offered by Retarus’ services comes into play.
By way of our Observability Metrics, for example, we grant your security and IT teams real-time insight into security-related data pertaining to your email communication. Changes in incoming volumes, quarantine rates, or authentication errors expose unusual traffic spikes at an early stage. In Prometheus format, this data can be integrated into existing monitoring and observability platforms such as Grafana, Splunk, Dynatrace, or Elastic. In this way, a flood of emails that would otherwise be difficult to interpret becomes a recognizable pattern that can be detected quickly.
myEAS Email Live Search, moreover, allows you to search within your email correspondence by sender, IP address, subject line patterns, and time periods.
Using SIEM integration, the data provided by Retarus can be easily correlated with data from Microsoft Teams, identity management systems, and endpoint systems. This enables security teams to recognize that the “flood of emails” and attempts by external persons to contact users are part of a single, coordinated attack.
Containing the wave of attacks – quickly and effectively
As soon as a wave of attacks wave has been identified, the Administration API facilitates an immediate response. The senders and domains involved can be blocked in real time using inbound restriction lists and anti-spam blocklists (for individual recipients or organization-wide). This gives your SOC team the opportunity to restrict further delivery without having to perform laborious, time-consuming manual configurations.
Retarus Transactional Email: Protect your outbound channel from misuse
Although “Inbox bombing” specifically targets email inboxes, the cases we’ve observed generally involvethe misuse of email delivery services. However, customers using Retarus Transactional Email can rest assured that technical and organizational measures are in place to prevent such attacks from being carried out in their company’s name. These measures include strictly controlled access and sending processes, continuous monitoring of email traffic, and clearly defined procedures for detecting and responding quickly to any form of irregular activity.
Retarus advises: Remain vigilant and react quickly to any suspicious activity
For the time being, keep a close eye on any unusual developments in your email traffic and sudden spikes in inbound volumes. At the same time, remind your employees of the best practices for handling suspicious attempts to contact them. Should you suspect that such an incident may have occurred at your company, please get in touch with our experts straight away. In addition to offering technical countermeasures, Retarus Support and our Professional Services teams are always at hand to assist and advise you when it comes to analysis, configuration, integration into existing security processes, and responding to incidents.


Submit a comment